Where to find it
Settings → Settings → Global → Call to action → Mode = Save / API → Webhook URL.
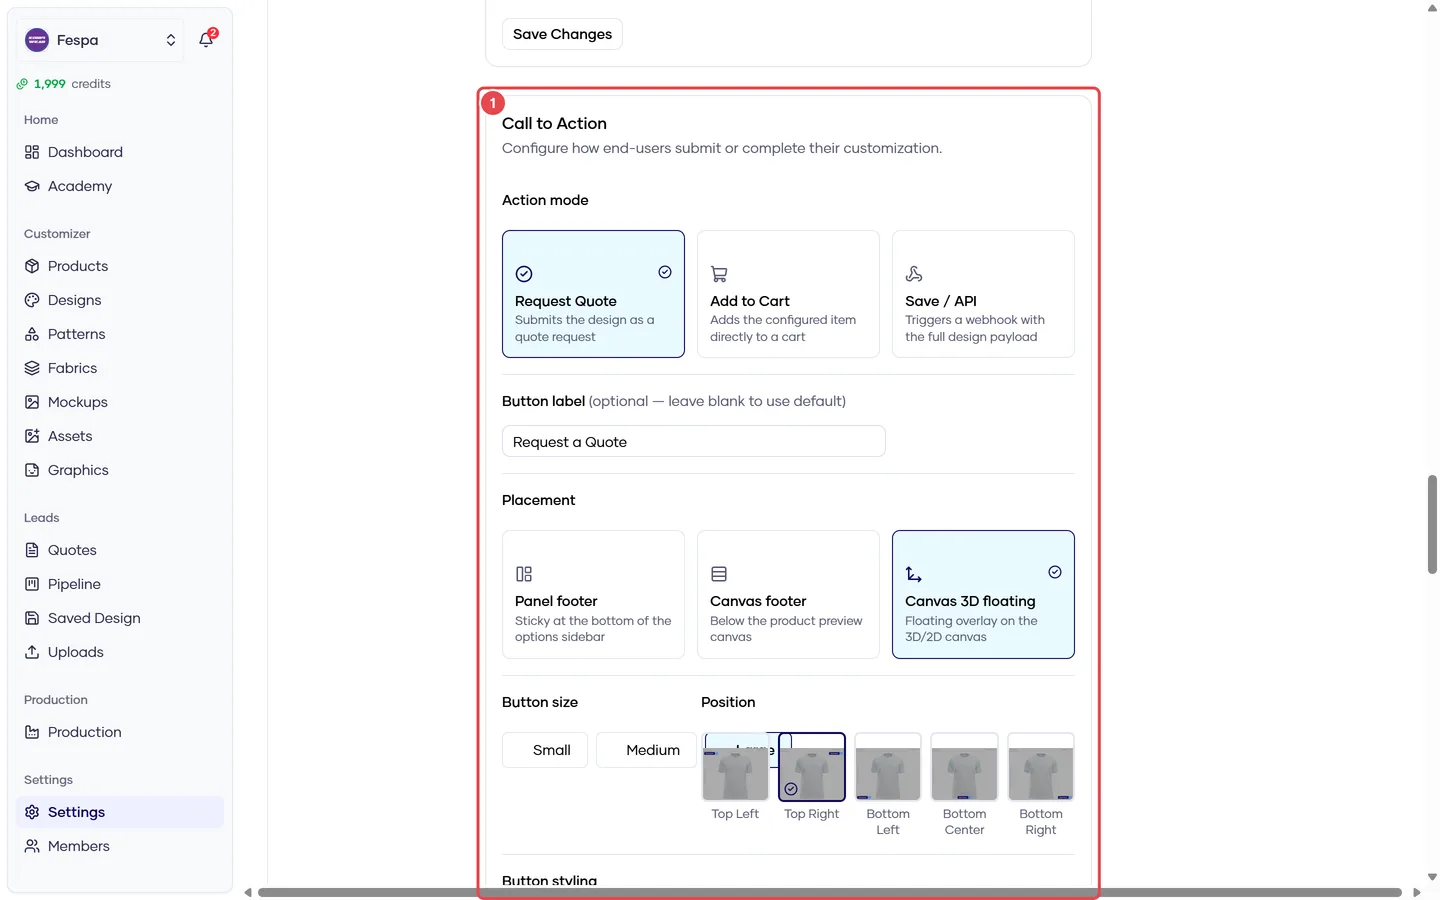
- Call to action: mode (Quote / Cart / Save API), placement, label, price summary, terms
What it does
When a customer clicks the storefront button in Save / API mode, Konfiwear stores the design and then POSTs a JSON payload (design.saved.v3) from its servers to your HTTPS endpoint. No browser CORS involved. Use it to create orders in your own ERP, headless shop or order-management tool.
Set up
- Switch the CTA mode to Save / API and paste your Webhook URL (HTTPS only; localhost and private IPs are rejected).
- Click Send test. Konfiwear posts a representative payload and shows the HTTP status, response time and any error text.
- Save.
Payload (overview)
{
  "event": "design.saved.v3",
  "transaction_id": "external-project-123",
  "session": { "id": "…", "product_count": 1, "passthrough": { "s": "…" } },
  "customer": { "name": "…", "email": "…" },
  "products": [
    {
      "product_code": "hoodie-classic",
      "design": { "id": "…", "preview_front_url": "…", "preview_back_url": "…" },
      "sizes": [{ "code": "M", "quantity": 12 }],
      "roster": [{ "name": "…", "number": "10", "size": "M" }],
      "pricing": { "unit_price": 42.0, "total": 504.0, "currency": "EUR" }
    }
  ],
  "quote": { "id": "…", "number": "Q-1042", "url": "…" },
  "assets": { "status": "ready", "print_files": [] }
}
transaction_idis whatever your page put on the iframe URL (?transaction_id=…) — use it to match the design to your own order or session.session.passthroughechoes query params you allow-listed under Session passthrough params. It is not verified — treat it like any user-supplied value.- Respond with a 2xx quickly (the request times out after a few seconds). A failed delivery is retried three times with a short backoff; after that the design is still saved in Konfiwear (Leads → Saved designs) and the quote detail shows the delivery error, so nothing is lost — but your endpoint must be reliable.
Security
When a webhook signing secret is configured for your workspace, each delivery carries an X-Konfiwear-Signature: sha256=<hex> header — an HMAC-SHA256 of the raw request body keyed with that secret. Verify it before trusting the payload. Ask support to set or rotate the secret if the card does not show one.
Common questions
I need events for quote status changes, not only saved designs. The full event set (quote confirmed, in production, completed) is part of the Enterprise plan. Contact us.
Retries create duplicates in my system. Deduplicate on quote.id (or session.id) — the same event is retried with the same ids.